Cyber tabletop exercises for real-world incident response
Most cyber tabletop exercises are a slide deck and a polite conversation. CMD is a live crisis.
This is a cyber resilience tabletop exercise built to put your incident response under pressure. Phones ring. Video calls connect. Information changes. Decisions change what happens next. Your team has to communicate, escalate and make the call while the incident keeps moving.
Because the first time you rehearse a cyber crisis shouldn't be when you're already in one.
13 ready-to-run scenarios, or build your own. See the scenarios →
A Tabletop You Walk Through Isn't a Rehearsal. It's a Meeting.
Annual, deck-driven tabletop exercises feel productive. The response plan makes sense. Everyone knows who they'd call. Decisions get made around a conference table with plenty of time to think.
But what about when a real incident hits? The cyber incident response plan suddenly depends on real people making difficult decisions under pressure.
Don't just discuss what they'd do. Make them rehearse it.
Three Things Make it Real
Ai Calls That Actually Connect
The phone in their pocket rings. The video call connects. On the other end is a convincing AI persona playing the attacker, the panicking supplier, the journalist chasing a story. Your team has to respond live, with no script to hide behind. This test is all about communication under pressure.
Decisions with Real Consequences
CMD doesn't wait politely for everyone to agree. Scenarios branch around the decisions your team makes. Pay the ransom? Brief the press? Every choice moves the cyber crisis simulation somewhere new, exposing what your team may actually have to face in the real world.
Evidence by Default
CMD captures every call, message, decision and escalation throughout the cyber tabletop exercise. At the end, you get a full debrief and a role-by-role report, giving you something concrete to examine instead of relying on somebody's meeting notes. Download the lot as a single PDF for your board, auditor or regulator.
Watch it unfold
Built to be watched, played and felt.
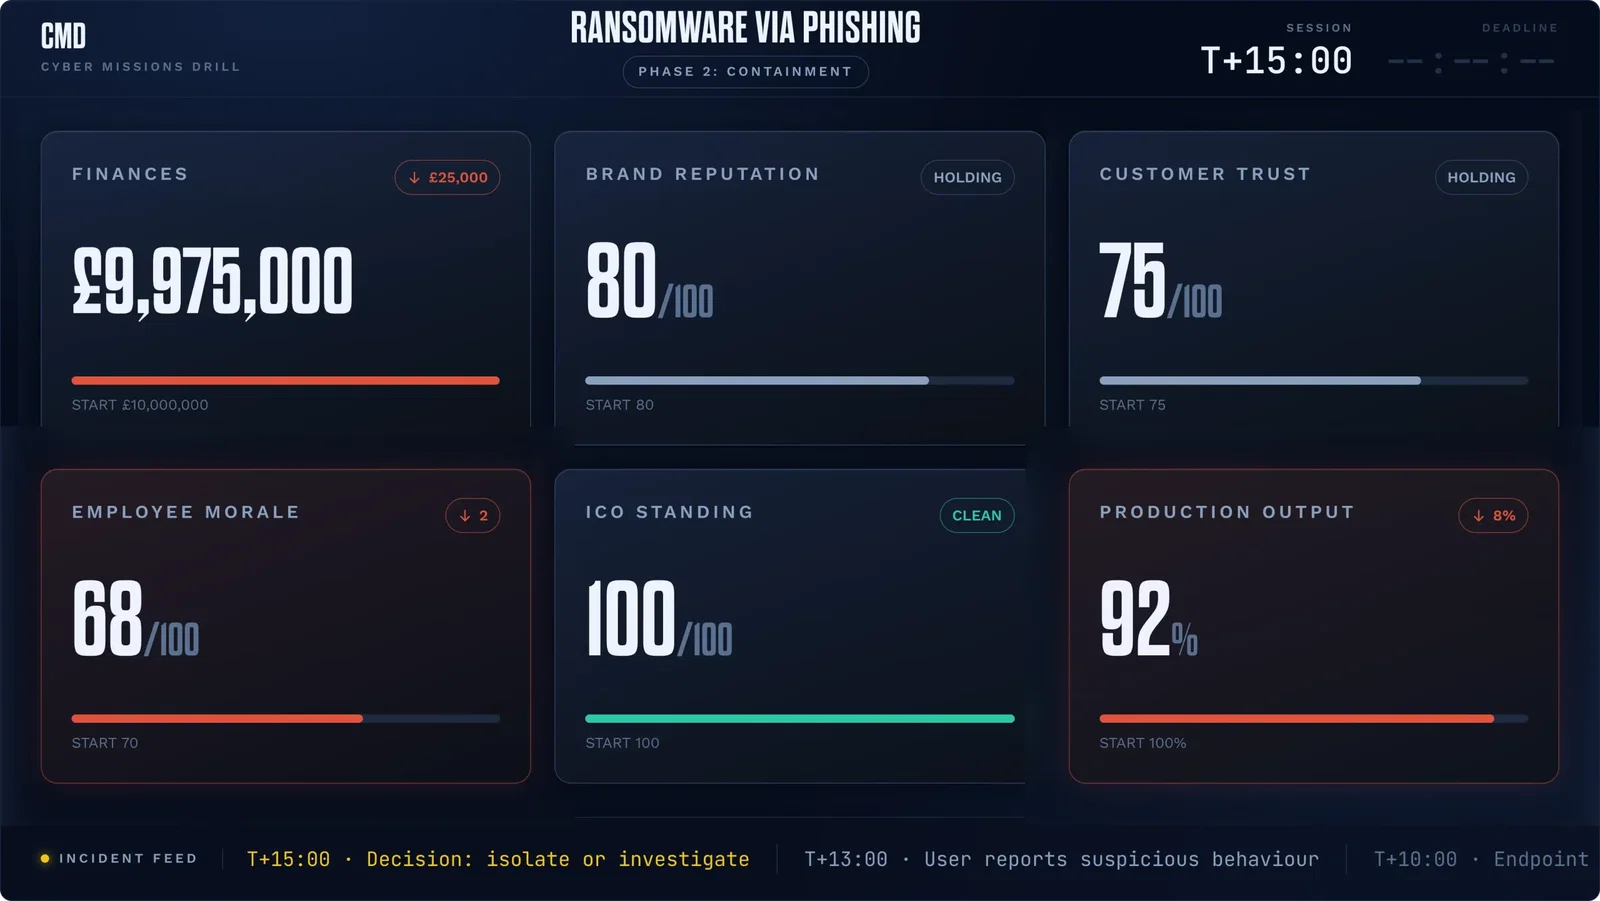
Watched
The incident plays out on the big screen in front of the whole room.
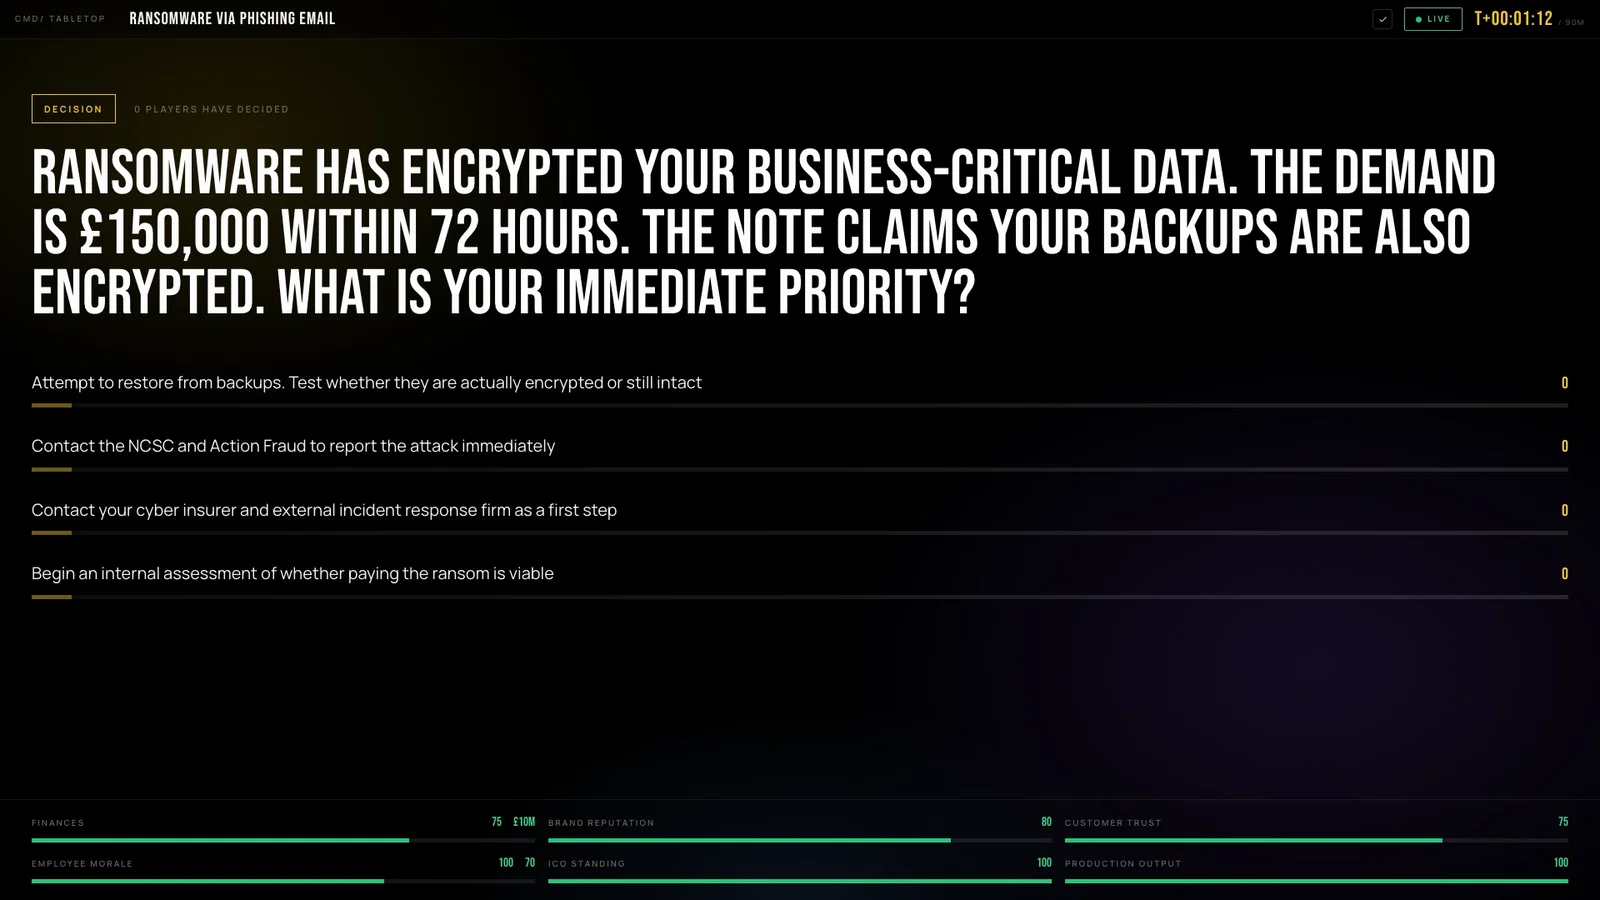
Played
Calls, messages and decisions land on your team's own devices.
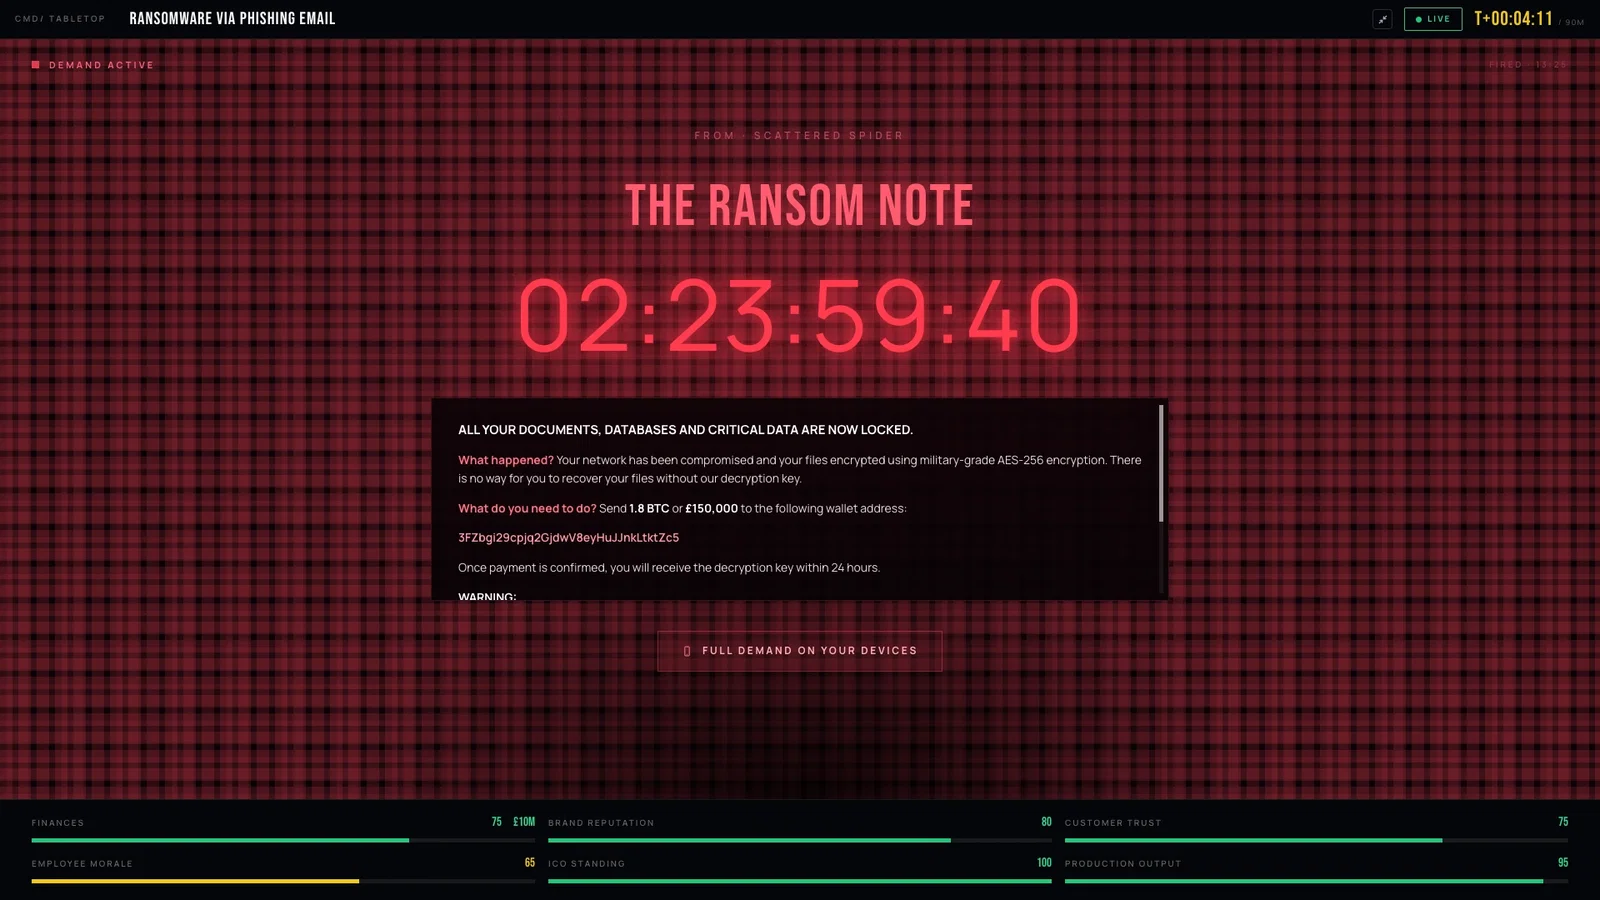
Felt
Pressure, uncertainty and consequences that don't wait for consensus.
A live cyber crisis, run in your room.
The Command Centre
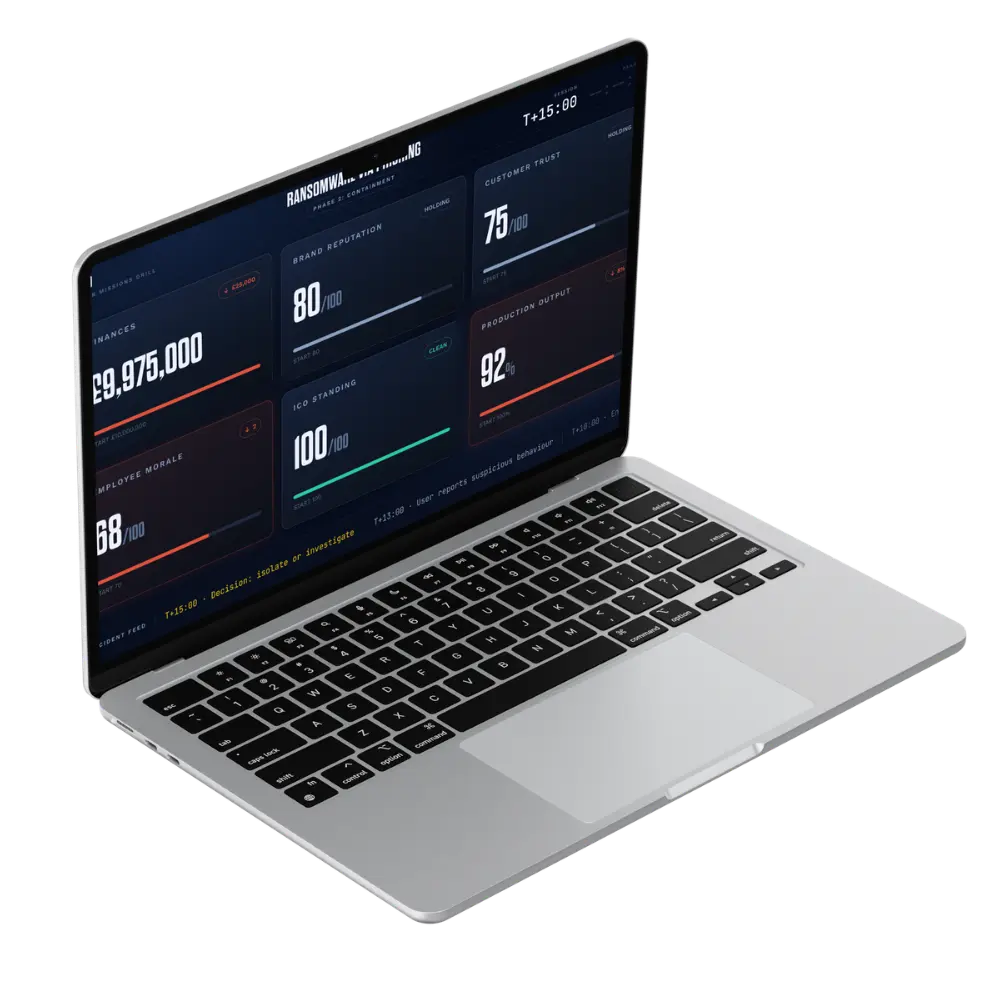
A trained facilitator runs the cyber incident response exercise from a live command centre, firing events, dialling up the pressure and watching every decision land in real time.
Player Devices
Your team joins through a browser on their own laptops or tablets. Calls land, messages arrive, and decisions need to be made. It's a cyber incident simulation they have to respond to in real time.
The Big Screen
While your team handles the incident, the bigger picture unfolds in front of them: breaking news, ransom notes, decisions. Everyone in the room sees things develop and decides what the hell to do about it.
The Mechanic
The Incident Comes At Them From Every Direction.
Each player works from a single inbox, with the whole incident playing out on the big screen beside them. This forces your team to prioritise, communicate, and make decisions under pressure.
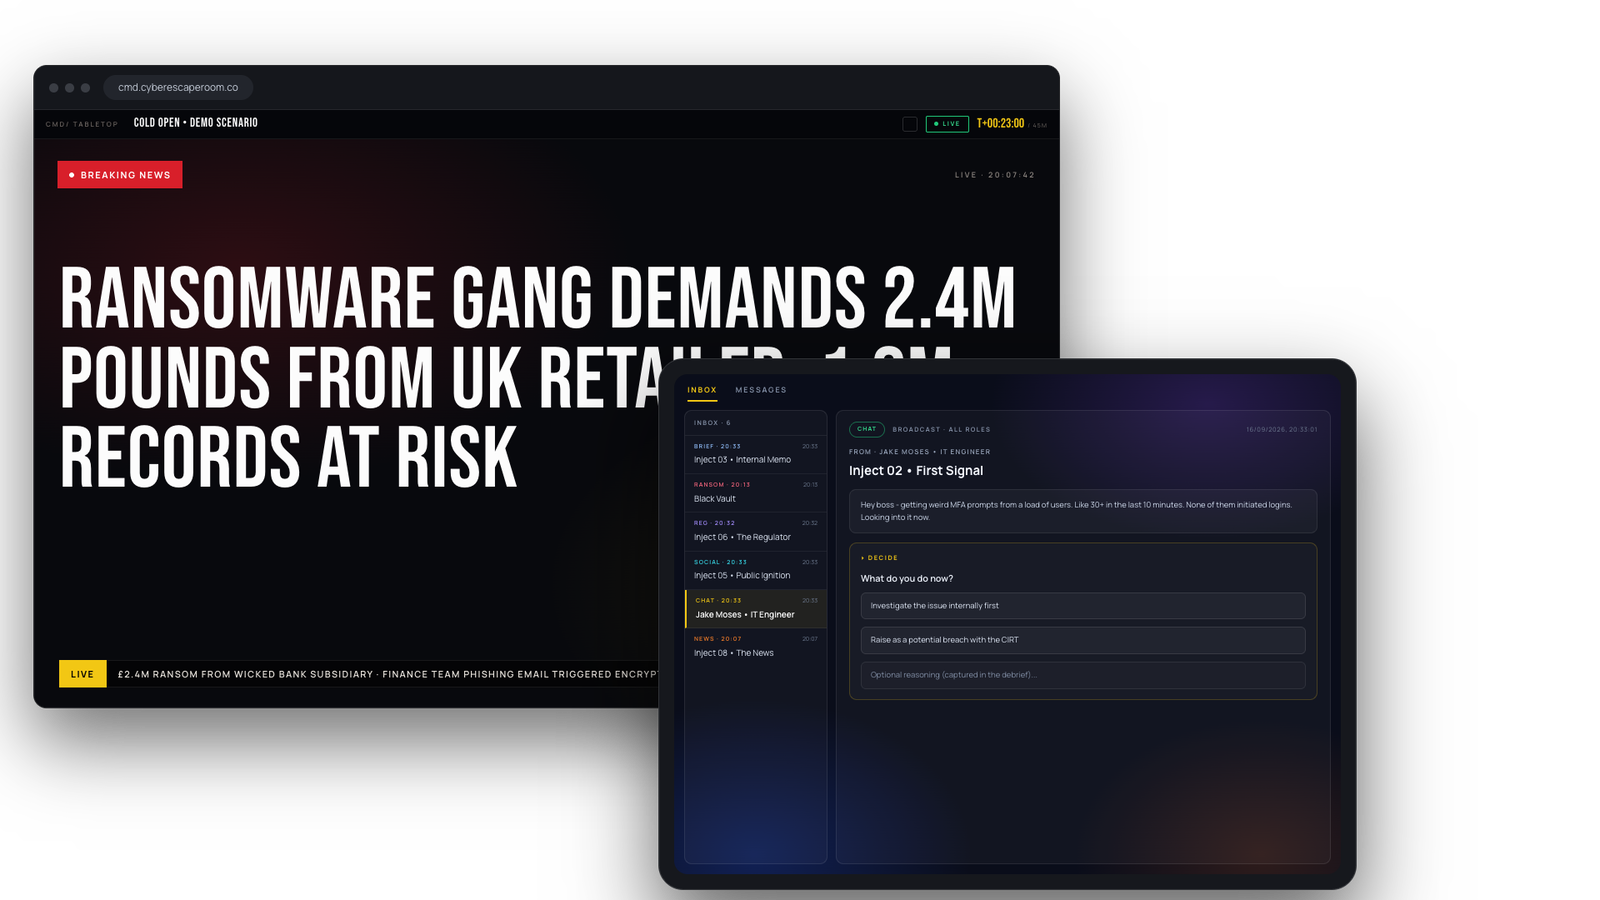
Does it reach the right person in time?
A crisis is won or lost on the hand-offs. In CMD, players forward and escalate anything they receive to whoever should see it next, building a real chain of command as the incident unfolds.
So you find out whether the phishing report actually reaches IT, whether IT escalates to the CISO, and whether Legal gets pulled in before the regulator does. Or whether it sat in somebody's inbox for a little bit too long...
Every hop is timestamped and captured, with the note attached at each step. How the team routed the threat lands in the debrief and the report, so good and bad escalation becomes evidence, not a guess.
Cyber resilience isn't just having a response plan. It's whether the right people recognise, escalate and act when the plan meets reality.
Built for the people who'll be in the room on the day.
A real incident is never just one team's problem. CMD is built for those who end up making the calls when it counts. Think C-suite and board leaders, incident leads, IT and security, Legal, Communications, and Operations teams.
From Rehearsal to Action
The cyber crisis ends but the work doesn't. Afterwards, you can debrief the decisions, calls, messages and escalations, finding the gaps and unanswered questions. Assign actions, update relevant plans and processes and decide what needs rehearsing again before a real incident finds the weak spot for you.
What should a tabletop exercise reveal?
Can your leaders communicate when things get messy? Does everyone know their role and responsibilities? Do escalation routes actually work? A meaningful cyber attack tabletop exercise should expose the gap between what the response plan says and what people actually do.
What a Cyber Crisis Actually Tests
A good cyber crisis simulation tests whether your people can protect business continuity, communicate across teams and follow escalation routes. It reveals their decision-making when information is incomplete or changing, and where the response needs more rehearsal.
The Scenarios
Thirteen cyber crisis tabletop exercises, ready to run.
Every scenario is a live incident, not a script. Calls land on your team's phones, the story branches on their decisions, and every message is mapped to the behaviour it's testing, so the report shows exactly where the response held and where it didn't. Pick one off the shelf for your next cyber security simulation exercise, or build your own.
Most run 60 to 75 minutes, with a shorter version for tighter diaries.
 01
Ransomware & Extortion
Ransomware via Phishing
One misspelled supplier domain, one opened attachment, six encrypted machines in thirty minutes, and a journalist on the line before lunch.
In the roomCEO · CFO · CISO · Comms · DPO
 02
Ransomware & Extortion
Supply Chain Ransomware
A trusted supplier's VPN tunnel, 70% of the estate encrypted by breakfast, a £480,000 demand, and a leak site that won't wait for your decision.
In the roomCEO · CISO · HR · Comms
 03
Ransomware & Extortion
Threatened Data Leak
An anonymous extortion demand, a data sample that's frighteningly real, and a deadline that keeps getting closer.
In the roomCEO · CISO · HR · DPO · Comms
 04
Suppliers & Third Parties
Supply Chain Attack
A critical HR platform goes quiet, the supplier won't say why, and by lunchtime 180 employees' bank details are in someone else's hands.
In the roomCEO · IT · DPO · Comms · Procurement
 05
Suppliers & Third Parties
Supply Chain Software Compromise
A trusted supplier, a routine update, six months of silent administrator access, and a customer asking four polite questions nobody can answer.
In the roomCEO · IT · HR · Comms
 06
Suppliers & Third Parties
Third-Party Software Compromise
A supplier you trusted is breached upstream, stolen credentials come back through your own front door, and the platform your customers depend on goes dark for three days.
In the roomCEO · IT · HR · DPO · Comms
 07
People & Devices
Insider Threat
A trusted employee, a personal USB drive, six weeks of transfers, and a competitor's pitch deck that should never have been public.
In the roomCEO · CISO · HR · Comms · Legal
 08
People & Devices
Mobile Phone Theft
One company phone left on the Tube, a six-digit PIN everyone trusts, an iOS update dismissed twice, and a supplier who wants answers in writing by close of business.
In the roomCEO · IT · Comms · Operations
 09
People & Devices
Bring Your Own Device
A personal laptop, a silent cloud sync, a six-week-old trojan, and an employee who did everything right until the organisation asked for his laptop.
In the roomCEO · IT · HR · Operations
 10
People & Devices
Home and Remote Working
A sudden move to remote working, a personal laptop, one convincing email, and four hours of overnight access nobody noticed.
In the roomCEO · CISO · HR · Comms · Line Manager
 11
People & Devices
Unknown WiFi Network
An account manager, a coffee shop, a WiFi network that isn't what it says it is, and two days of access before anyone notices.
In the roomCEO · IT · Operations · HR
 12
Disclosure & Sustained Threat
Vulnerability Disclosure
One social media DM, one marketing inbox, 22 hours of silence, and a phishing page on your own domain.
In the roomCEO · CISO · Comms · Legal · Customer Success
 13
Disclosure & Sustained Threat
Heightened Cyber Threat
Five weeks of escalating threat, no confirmed breach, and an organisation that has to find out whether it has the structures and the stamina to live under pressure.
In the roomCEO · CISO · Operations · HR · Comms
Scenario builder
Don't see your risk? Build it.
Write your own incident in the scenario builder, with your systems, your suppliers and your people. Or we'll build one with you around your sector and the risks that keep you up at night.
Request a demoNot sure which fits? Tell us what keeps you up at night and we'll match you to a scenario, or build one with you.
Take something with you
Three things worth reading before you put your leadership through an incident.
Why Most Tabletop Exercises fail
The four habits that will turn a resilience test into a meeting, and what to do instead.
An Example CMD Report
The real output of a session: decisions, calls, escalation chains and timings, role by role.
Run your own tabletop exercise
A scenario, injects timeline and a debrief structure you can run yourself, no facilitator required.
Cyber Resilience Tabletop Exercises, Run live.
A cyber resilience tabletop exercise rehearses how an organisation responds to a cyber incident. CMD makes that rehearsal live, putting communication, escalation and decision-making under pressure rather than simply discussing a hypothetical scenario.