39%
Of incidents IBM X-Force investigated in Europe hit finance and insurance. The most targeted sector on the continent.
IBM X-Force Threat Intelligence Index (2026)
$6.29M
Average cost of a breach in financial services. 26% above the global average.
IBM Cost of a Data Breach Report (2026)
62%
Of breaches involve the human element.
Verizon Data Breach Investigations Report (2026)
Trusted by
The Problem
Why traditional security awareness training falls short in banking
96%
of employees who took a risky security action
knew it was risky at the time.
Proofpoint state of the phish (2024)
Knowing the risk isn't the problem.
Banking knows how to manage risk. You model it. Stress-test it. Put controls around it. Employ entire teams to work out where things could go wrong before they actually do.
Then the annual cyber module turns up. Twenty minutes of e-learning might tell somebody what a phishing email looks like. It doesn't tell you what they'll do when the message looks legitimate, comes from somebody senior and lands while they're trying to get six other things finished.
They know what to do. But they do the other thing anyway. That gap between knowing and doing is where incidents happen.
A completed course doesn't tell you what happens next
Completion rates have their place. They show the training happened. They don't show how somebody responds when the caller sounds convincing, the payment request is urgent or a perfectly normal process suddenly feels slightly off.
A randomised study of 19,500 employees found a 1.7% difference between people who'd done their annual training and people who hadn't. (Ho et al. 2025).
People need somewhere to practice the decision, and somewhere safe to get it wrong.
Cyber Security in Banking: What your people are actually up against.
The threats change. The human bit is remarkably consistent. Somebody creates urgency, borrows authority or makes an unusual request sound completely reasonable. Your people have to decide what happens next.
01
£41.3M
Invoice & Mandate Fraud, Uk 2025
Business email compromise
A supplier changes their payment details. An executive needs something approved immediately. The email looks right. The language sounds right. Nothing is screaming SCAM.
UK Finance recorded £41.3m lost to invoice and mandate fraud in 2025, across 2,305 cases. That's close to £18,000 every time one gets through. Rehearsal lets people practice slowing the situation down, checking the request and challenging it when the pressure is on.
Uk finance Annual Fraud Report (2026)
02
+40%
Click rate, voice & text vs email
Vishing & Voice Fraud
A convincing phone call creates the same pressure as an email, only faster, particularly when the person at the other end of the line sounds like they know the business. Criminals impersonating police and bank staff took £55.5m from UK victims in 2025.
CTRL+Vish puts your people into a live conversation with an AI-powered visher. No script to read. No answer conveniently waiting on screen.
Verizon DBIR (2026) • UK Finance (2026)
03
Third Party & Supply Chain
Trusted suppliers and partners create their own set of decisions. Has this access request changes? Is that instruction normal? Does this person actually need what they're asking for?
Employee training doesn't replace technical third-party risk management, and we're not pretending it does. But your people still need to recognise when something doesn't add up, and know when to stop, check and escalate.
04
Insider Risk
Not every insider incident starts with malicious intent. People can be manipulated. Processes can be misunderstood. Someone can follow an unusual request because it sounds credible enough in the moment.
Security culture matters when an employee feels able to question that request, even when the person asking is more senior. They shouldn't need the policy document open in another tab before they feel allowed to say, "Hang on."
Cyber resilience in
financial services:
DORA raised the bar
For financial organisations in scope of the Digital Operational Resilience Act, people sit inside a much wider operational resilience picture. In the UK, the PRA and FCA operational resilience rules have applied in full since March 2025.
Training matters. So do policies, testing and documented controls. But a completion report still can't tell you what somebody will do during an incident. That takes practice. If you want people to recognise the warning signs and make sensible decisions under pressure, they need a chance to do it.
Article references follow the final DORA text (Regulation EU 2022/2554), applicable from January 2025.
The Alternative
Training the instinct. Not the tickbox.
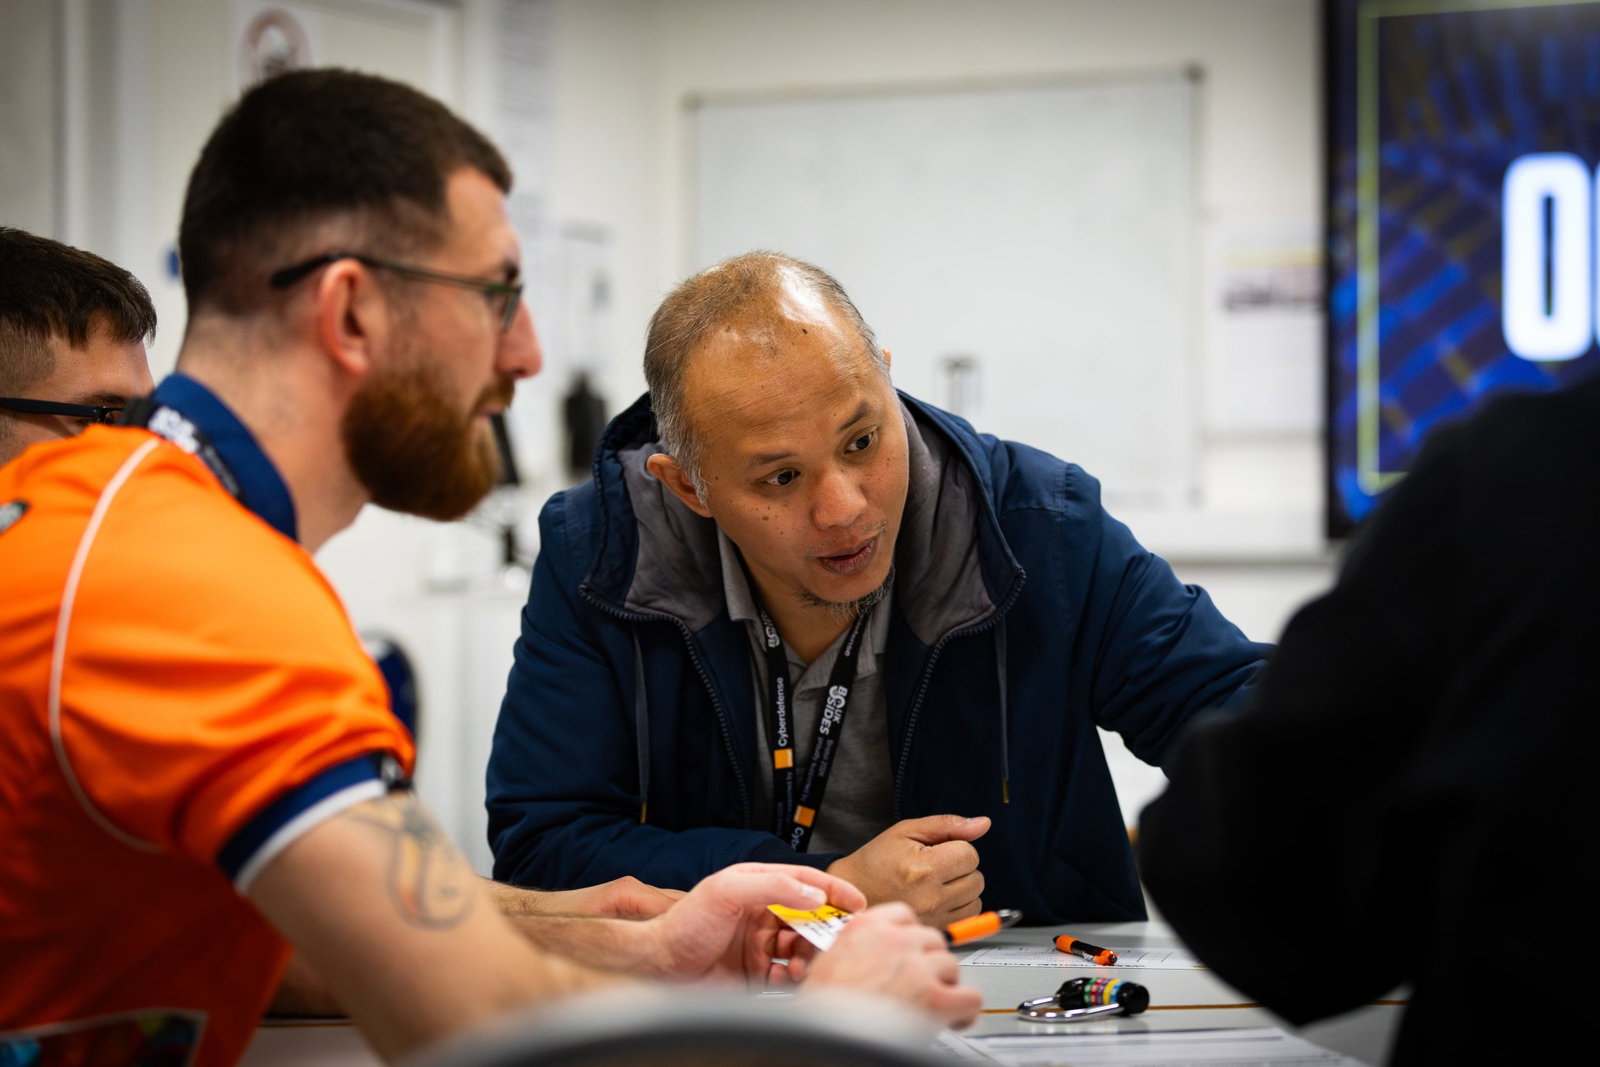
Our experiences put people into the scenario instead of explaining it to them afterwards. Physical escape rooms. Digital experiences. AI-powered vishing calls. Large-scale events. Tabletop exercises.
The format depends on the people and the risk. What doesn't change is the rehearsal. That gives you something far more useful than a quiz score. You get to see how people behave.
Different teams. Different risks. Different rehearsals.
A bank might need to reach payment teams, regional branches, contact centres, remote workers and senior leadership. They don't all face the same decisions, so there is little point giving them all the same experience.
Put your team inside the incident
Small groups work through credential theft, executive impersonation, social engineering and insider risk under time pressure. The debrief afterwards is where you unpack those decisions and turn the experience into something useful.
Explore ESC →Scale it across every branch, every team
The same scenario-led approach, delivered digitally as story-driven campaigns through the year. Built for branch networks, contact centres and several thousand people who won't fit in one building.
Explore SHIFT →Put your people on the phone with the threat
Finance. Treasury. Payments. Relationship management. The people in high-risk roles get an AI-powered visher in real time, then the risk scoring shows you where more work may be needed.
Explore CTRL+VISH →Run the incident before it runs you
A live, facilitated crisis simulation for senior leaders and incident teams. AI calls land on their own phones, decisions branch, and the After Action Report shows where the response held and where it didn't.
Explore CMD →Security awareness training built around banking risk
There is no single version of human risk in banking. So start there. What do you need people to do differently? Then build around that behaviour.
The measure that matters is whether people are better prepared when the real situation turns up.
Explore experiences →Ready to stop ticking boxes?
Tell us what you're trying to change. No long-winded sales process. No
generic training package pulled off the shelf. Just a proper conversation
about the risk, the people involved and what they need to practice.